SOC online 24/7Breach or outage? Call 858-399-4225

Free guidesinfo@alpiba.comMon–Fri, 7am–7pm PT

Alpiba

Why Alpiba

Enterprise discipline. Small-business pricing.

Three promises shape everything we do: fast response, strong cybersecurity and predictable costs. Here's what each one means in practice.

Promise 01

Fast response.

Callers reach a senior engineer, not a call queue. Our SOC responds in minutes, any hour, and triggers a containment playbook within the first hour of a ransomware or breach event.
  • Senior engineers answer the phone
  • 24/7 SOC for managed clients
  • Containment within the first hour
Server racks in a dim data center with status lights

Promise 02

Strong cybersecurity.

Security and IT are built as one system. Real analysts, real playbooks and a tuned SIEM, MDR and identity stack watch your endpoints, identities, email and cloud.

  • Managed EDR / XDR
  • MFA and zero trust everywhere
  • Immutable backups tested quarterly
A close view of a glowing circuit board

Promise 03

Predictable costs.

One flat, per-user monthly price with no surprise line items, scoped after a free 30-minute assessment, so your IT budget stays predictable as you grow.
  • No hourly surprise bills
  • Unlimited helpdesk tickets
  • Quarterly budget reviews
Two business partners reviewing plans together at a laptop

Compare

How Alpiba compares to other IT models.

Alpiba managed IT compared with break-fix IT and one in-house generalist
What you getAlpiba managed ITBreak-fix ITOne in-house generalist
PricingFlat per-user monthlyHourly, after problemsSalary plus tools
Security monitoring24/7 human SOCNoneBusiness hours
Incident response<15 min first responseWhen a tech is freeDepends on availability
BackupsImmutable, tested quarterlyRarely testedVaries
Compliance supportSOC 2, HIPAA, NIST evidenceNot includedLimited
CoverageCloud, network and security specialistsWhoever is dispatchedOne person, vacations included

Read the full guide

More reasons

Why teams switch to Alpiba.

One partner, full coverage

Security and IT built as one system. No gaps between vendors and no blame-shifting.

Enterprise discipline

Fortune 500 and public sector experience, 25+ years in technology and a CIO Diamond Award recipient in leadership.

Certified engineers

Microsoft 365 and Google Workspace certified engineers for migrations, hardening and administration.

Outsourced or co-managed

Use Alpiba as your full IT department, or as backup for the IT team you already have.

Local and on-site

San Diego-based, with on-site and remote support and 24/7 monitoring for distributed teams.

Plain-English communication

You always know what happened, what we did and what's next.

Industries we serve

Built for the industries we know best.

All industries
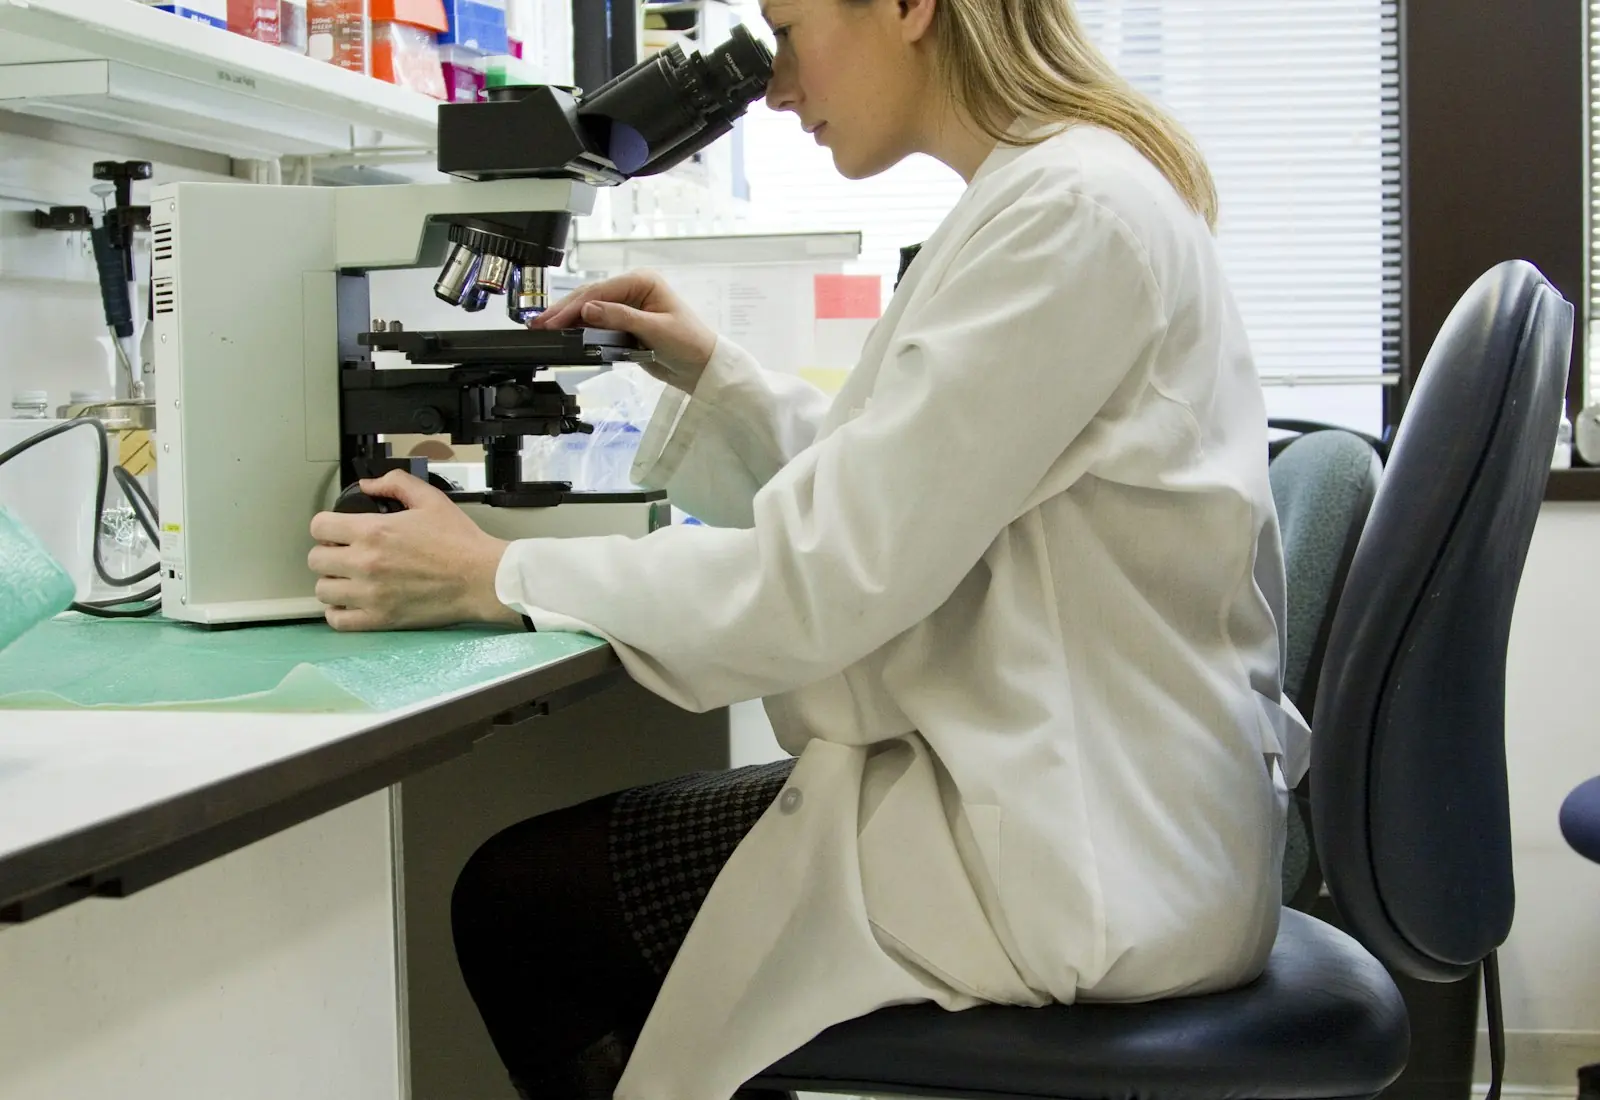
A scientist using a microscope at a laboratory bench

Biotech

Protect research IP, lab instruments and audit-ready data.

IP protection · Lab uptime
Law books on dark library shelves

Legal

Confidential files and secure access from anywhere.

Confidentiality · Remote access
An empty dental treatment room with a chair, monitor and cabinets

Dental

HIPAA-aligned safeguards for patient records.

HIPAA · Patient data

Why we built Alpiba

“SMBs deserve a strategic technology partner, without enterprise complexity or cost.”

Roopa · Founder, Alpiba · former Accenture advisor

Fast response, strong cybersecurity and predictable costs: the three promises behind every Alpiba engagement, backed by enterprise experience and delivered with a boutique firm’s attention.
Roopa, founder of Alpiba, standing in front of evening city lights

In depth

How to choose a managed IT provider in San Diego.

8 min readBy the Alpiba teamUpdated October 15, 2026

On this page

Choosing a managed IT provider in San Diego is one of the few vendor decisions that touches every person, device and file in your business. Get it right and IT fades into the background. Get it wrong and you find out during an outage, an audit or a ransomware attack.

This guide sets out what a modern managed service provider (MSP) should deliver, how the main support models compare, the questions worth asking and the red flags worth walking away from. Where it helps, we show exactly how Alpiba does it, so you have a concrete benchmark for every provider you talk to, including us.

What to expect from a modern MSP

Managed IT used to mean a helpdesk and remote fixes. Today security, cloud administration and recovery planning are part of the job, because that's where the real business risk sits. This is the baseline to insist on when choosing a managed IT provider in San Diego, or anywhere else.

  • Security in the base service. MFA, managed EDR, email protection and patching are part of the standard package, with people, not just software, watching alerts around the clock.
  • Response you can measure. You know the average first response time, what happens after hours and who picks up when you call.
  • Recovery that's been tested. Backups are only as good as the last successful restore, so you see restore results, not just backup job reports.
  • Documentation you can see. Network diagrams, runbooks and account inventories are written down and available to you, not locked in one engineer's head.
  • Strategy, not just tickets. Regular reviews connect technology decisions to your plans, budget and risk.
  • Pricing that holds still. A clear monthly price that doesn't climb every time your team asks for help.

How Alpiba stays accountable

Accountability is easy to claim and hard to fake, so here are the specifics behind our three promises: fast response, strong cybersecurity and predictable costs.

Our response model
SituationWhat happensWho handles it
A security alert, any hourAverage first response under 15 minutesHuman analysts in our 24/7 SOC
Ransomware or a breachA documented containment playbook is triggered within the first hourOur SOC, working from a written playbook
An everyday IT requestUnlimited helpdesk tickets, with an average first response under 15 minutesOur helpdesk engineers
You call the office lineStaffed Monday to Friday, 7am to 7pm Pacific, with 24/7 support for managed clientsA senior engineer, not a call queue
A new inquiryA reply within 12 to 24 hoursOur team, with a senior engineer for scoping

Playbooks, not improvisation

We write things down. Your environment gets documentation and runbooks, onboarding and offboarding follow a defined workflow, and incident response follows a containment playbook rather than whoever happens to be awake. Written process is what makes a 3am response as consistent as a 3pm one.

Quarterly reviews you'll actually use

Every quarter we review risk, incidents, the roadmap and the budget with you, then agree priorities for the next one. It's where strategic advice happens, and where you can hold us to what we said last time. The people and values behind these commitments are part of the story behind Alpiba.

Comparison of Alpiba managed IT, break-fix IT and one in-house generalist across pricing, security monitoring, incident response, backups, compliance support and coverage. Alpiba offers flat per-user pricing, a 24/7 human SOC, under-15-minute first response and tested immutable backups.
Managed IT vs break-fix vs one in-house hire.

In-house, break-fix, managed or co-managed?

There are four common ways to run IT. Each can work, and each fails in predictable ways. The right fit depends on your size, your risk and whether you already have IT people you value.

The four IT support models at a glance
ModelHow it worksFits best whenWhere it breaks down
In-house ITYou employ your own IT staffYou need someone on site daily and can fund a teamOne person can't cover security, cloud and helpdesk, or be on call 24/7
Break-fixYou pay by the hour when something breaksYou have very few devices and little sensitive dataNobody watches between calls, and costs spike during incidents
Fully managedA provider runs IT and security for a monthly feeYou want predictable costs and 24/7 coverage without hiringThe provider is reactive or vague about response and security
Co-managedYour IT staff and a provider share the workYour team is capable but stretched, or short on security depthResponsibilities aren't written down and agreed

We offer both fully managed IT and co-managed IT, so the recommendation we make in your assessment is about fit, not about which model we sell.

Security-first, in practice

Plenty of providers sell security as an add-on. We treat it as the way IT gets done, designed into every recommendation, migration and script from the first day rather than added at the end. Four commitments apply to every environment we manage.

Identity first

MFA and zero-trust access everywhere we manage, so a stolen password alone opens nothing. Access depends on who you are, the health of your device and the context of the sign-in.

Humans on watch 24/7

Managed detection and response on every endpoint, plus a human-staffed SOC watching identities, email and cloud. Analysts investigate and contain threats instead of just forwarding alerts.

Recovery you've rehearsed

Immutable off-site backups that ransomware can't alter, with restore drills every quarter. With a typical recovery time objective under 4 hours, a bad day stays a bad day instead of a lost week.

Encryption by default

Data is encrypted in transit with TLS 1.2 or higher and at rest with provider-managed encryption. It's the baseline, not an upgrade.

Readiness, not rubber stamps

Our compliance readiness work helps you put in place, and prove, the controls behind SOC 2 Type II, HIPAA, NIST CSF, ISO 27001 and PCI DSS. That's readiness for your business, not a certification of Alpiba, and the reports themselves come from independent auditors.

Alpiba's four-step process: 1. Discovery & Analysis, 2. Solution Design, 3. Implement and 4. Protect & Optimize.
How Alpiba works, from first call to fully protected.

What predictable costs really mean

Predictable pricing isn't the same as cheap pricing, and it shouldn't be vague either. Here's how ours works.

  • Flat, per-user, monthly. One price per person covers the managed service, so your bill tracks headcount rather than how many things broke.
  • Scoped before you commit. We scope your plan after a free 30-minute assessment, based on your people, systems, security needs and locations.
  • Unlimited helpdesk tickets. Your team can ask for help as often as they need. Nobody has to ration calls to protect the budget.
  • No surprise line items. Larger one-time projects, such as a migration or a new office network, are scoped up front so the cost is known before work begins.
  • Reviewed every quarter. Budget is part of each quarterly business review, so renewals, refreshes and growth are planned rather than discovered.

Comparing quotes? Run the same four checks with every provider, including us.

  1. Give everyone the same scope. List your people, devices, locations and any compliance or insurance requirements, so every quote prices the same work.
  2. Ask what the base price includes. Confirm whether 24/7 security monitoring, EDR, email security and backups are included or billed separately.
  3. Test the growth math. Ask what happens to the price when you add people, open a site or need a one-time project.
  4. Check the after-hours story. Find out who responds at night and on weekends, and whether that coverage costs extra.

Our guide to managed IT vs break-fix vs in-house covers the cost trade-offs in more depth.

Questions to ask any provider

Use these in every conversation, including with us. A good provider answers specifically and is happy to put the answers in writing.

  • What is your average first response time, and how do you measure it?
  • Who reviews security alerts overnight and on holidays: people, or only software?
  • What happens in the first hour of a ransomware event, and is that playbook written down?
  • When did you last run a test restore for a client, and what did it prove?
  • Is MFA enforced on every account you manage, including your own admin access to our systems?
  • What exactly is included in the monthly price, and what is billed as a project?
  • Who is our main point of contact, and can we reach an engineer directly?
  • How do you document our environment, and can we see that documentation at any time?
  • How will you help us answer cyber insurance and customer security questionnaires?
  • If we part ways, how do you hand back accounts, documentation and admin access?

If you're choosing a managed IT provider in San Diego, add two local questions. Can you be on-site at each of our locations, whether that's an office in Mission Valley, a lab in Sorrento Valley or a warehouse in Otay Mesa? And how do you plan for SDG&E Public Safety Power Shutoffs and wildfire evacuations?

Put us to the test

Bring this list to a free 30-minute assessment and ask us every question on it. You'll be talking to a senior engineer, not a salesperson.

Red flags to walk away from

  • Vague response promises. “We're very responsive” is not a number. Ask for an average first response time and how after-hours alerts are handled.
  • Security as an optional extra. If MFA, EDR or monitoring cost extra, they're easy to cut when budgets tighten, which leaves gaps exactly where attacks start.
  • Backups nobody tests. A provider who can show backup reports but not restore results is asking you to trust a hope.
  • Shared or anonymous admin accounts. Every engineer should use named, MFA-protected access, and you should be able to see who holds admin rights to your systems.
  • Pricing that punishes asking for help. Per-ticket fees and hourly overages discourage people from reporting problems early, when they're cheapest to fix.
  • Compliance overpromises. No provider can make you compliant or certified on its own. Auditors issue reports, and obligations such as HIPAA compliance stay with your business.
  • Blame-shifting between vendors. If every outage is someone else's fault, nobody owns the outcome.

What the first 90 days should look like

A provider's first quarter tells you most of what you need to know about the relationship. The plan below mirrors our own four-step process and makes a fair benchmark for any provider. Exact timing flexes with your size and what discovery uncovers.

A first 90 days you can verify
PhaseWhat happensWhat you should see
First 30 daysDiscovery & Analysis: users, devices, accounts, vendors and backups inventoried, and urgent gaps such as missing MFA closedA clear summary of risks and quick wins
Days 31–60Solution Design and Implement: roadmap agreed, then monitoring, EDR, email security and backups rolled out in tight windowsAn agreed roadmap and far fewer unknowns
Days 61–90Protect & Optimize: patching on schedule, a test restore, documentation and runbooks in placeRestore results, current documentation and your first quarterly business review

If a provider can't describe its first 90 days this concretely, keep asking questions before you sign anything.
Illustration of the San Diego skyline at sunset, with downtown towers, the bridge across the bay, sailboats and palm trees
San Diego, where Alpiba is based.

FAQ

Why Alpiba questions, answered.

Straight answers to the questions we hear most. Still curious? Talk to a senior engineer.

What should I look for when choosing a managed IT provider in San Diego?

Look for specifics rather than adjectives: a stated average first response time, people watching security alerts 24/7, security controls included in the base price, tested backups and documentation you can see. Local presence matters too, because some work needs someone on site somewhere in San Diego County. Ask how they would support each of your locations and how they plan for wildfire-season power shutoffs.

How fast does Alpiba respond?

Our average first response is under 15 minutes, and our human-staffed SOC monitors managed clients 24/7. An active ransomware or breach event sets off a documented containment playbook within the first hour. On weekdays from 7am to 7pm Pacific you can also call the office line, and we answer new inquiries within 12 to 24 hours.

Who answers when I call Alpiba?

A senior engineer, not a call queue. Whether you're dealing with an active incident, scoping a migration or asking about a security assessment, the person who picks up can actually help. The number is 858-399-4225, staffed on weekdays from 7am to 7pm Pacific, and managed clients have 24/7 monitoring and support outside those hours.

How does Alpiba keep IT costs predictable?

Through flat, per-user monthly pricing with no surprise line items. We scope the plan only after a free 30-minute assessment, so it fits your environment, and the helpdesk has no ticket limits or per-call fees. Budget is a standing item in every quarterly business review, and one-time projects are priced up front, so nothing appears on an invoice you didn't expect.

What's the difference between managed IT and co-managed IT?

With managed IT, the provider acts as your entire IT department. With co-managed IT, your internal staff stay in place and the provider fills the gaps, commonly round-the-clock security monitoring, cloud and network specialists, extra hands for projects and coverage when your own people are off. Alpiba offers both, and in a co-managed setup your team keeps ownership of daily priorities.

Is a managed IT provider cheaper than hiring an IT employee?

It depends on what you need covered. One in-house hire brings salary, benefits, tools and training costs, and still can't cover security, cloud, networking and the helpdesk around the clock. A managed provider spreads that work across a team for a predictable monthly fee. The fair comparison is total cost against the coverage you actually get, including nights and vacations.

What are the biggest red flags when choosing an MSP?

The biggest red flags are vague response promises, security sold as an optional extra, backups that are never test-restored, shared admin accounts, pricing that charges every time you ask for help, and claims that the provider can make you compliant on its own. Any one of these suggests a provider optimizing for its own convenience rather than your risk.

What happens in the first 90 days with Alpiba?

We follow our four-step process. Discovery & Analysis inventories your users, devices, accounts and vendors and closes urgent gaps. Solution Design and Implement put monitoring, EDR, email security and backups in place with minimal disruption. Protect & Optimize then keeps patching on schedule, proves recovery with a test restore and brings your first quarterly business review. Exact timing depends on your size.

Can we switch IT providers without disrupting the business?

Yes, with planning. We start by gathering documentation, accounts and admin access, then coordinate the handover with your current provider and vendors so nothing is left without an owner. Changes go live in tight windows with minimal disruption, and security basics such as MFA and monitoring are prioritized early in the transition rather than saved for later.

Can Alpiba make us SOC 2 or HIPAA compliant?

No provider can do that on its own, and you should be wary of any that claims to. We build the technical controls for SOC 2 Type II readiness and HIPAA-aligned safeguards, write them up and keep the evidence organized for review. Independent auditors issue SOC 2 reports, and HIPAA compliance remains your organization's responsibility. Alpiba itself is not certified against these frameworks.

What makes Alpiba different from other MSPs?

Three things you can verify: response you can measure, security built into the base service and pricing that doesn't move when you ask for help. Our human SOC averages under 15 minutes to first response, MFA and zero trust are standard everywhere we manage, backups are immutable and tested quarterly, and callers reach a senior engineer. Leadership brings Fortune 500 and public sector experience.

Free 30-minute assessment

See the difference in 30 minutes.

Tell us a little about your business. A senior engineer will map your top risks, quick wins and a right-sized plan, with no obligation and no sales pressure.

  • A senior engineer, not a salesperson
  • Reply within 12–24 hours
  • Flat per-user pricing if you want our help
Roopa, founder of Alpiba

Founder-led and San Diego basedRoopa founded Alpiba to give growing businesses a real technology partner.

858-399-4225Mon–Fri, 7am–7pm PT · 24/7 for managed clients
info@alpiba.comReply within 12–24 hours

Fields marked * are required. By submitting, you agree that Alpiba may contact you about your request. We reply within 12–24 hours; for an active incident, call 858-399-4225.

Call Free assessment