
Managed IT
Managed IT & White-Glove Support
Your single point of contact for all technology, with a tailored helpdesk and on-site support backed by clear SLAs.
SOC online 24/7Breach or outage? Call 858-399-4225
Free guidesinfo@alpiba.comMon–Fri, 7am–7pm PT
FAQ · 45 answers
The questions we hear most from San Diego founders, operators and IT leaders exploring a managed partner.
Call 858-399-4225 or email info@alpiba.com. We reply within 12–24 hours.
Alpiba is a San Diego managed IT and cybersecurity provider. We run your helpdesk and on-site support, monitor your endpoints, identities, email and cloud through a 24/7 human SOC, manage Microsoft 365 and Google Workspace, design networks and servers, and run immutable backups and disaster recovery, all for a flat per-user monthly price.
Alpiba is based in San Diego, California. We support businesses across San Diego County, including Downtown, Sorrento Valley, UTC, La Jolla, Carlsbad, Del Mar, Escondido, Oceanside and Chula Vista, and we serve remote and multi-site clients beyond San Diego through remote support and 24/7 monitoring.
We specialize in regulated and data-sensitive businesses: biotech and life sciences, legal practices, manufacturing and logistics, software and technology companies, and dental practices. These sectors share strict confidentiality, uptime and compliance requirements, which is where our security-first approach matters most.
Alpiba's leadership brings 25+ years in technology, Fortune 500 and public sector experience, more than 100 successful technology initiatives, over $100M in technology programs managed and 10,000+ end users supported. Our leadership is a CIO Diamond Award recipient.
Alpiba was founded by Roopa, whose career began inside corporate IT departments before Accenture recruited her in 2018 to advise large enterprises on strategy, cybersecurity and digital transformation. She started Alpiba to bring that enterprise discipline to small and mid-sized businesses, with the responsiveness, warmth and directness of a boutique firm. In her words: “SMBs deserve a strategic technology partner, without enterprise complexity or cost.”
It means getting the discipline large organizations rely on, without their complexity or cost. In practice that looks like documented systems, security designed in from the start, tested backups, clear response targets, quarterly reviews of risk and budget, and decisions mapped to recognized frameworks such as the NIST Cybersecurity Framework. Our leadership brings Fortune 500 and public sector experience, applied at the scale of a growing business.
Both. As a managed service provider, we run day-to-day IT and security for a flat per-user monthly price, either as your full IT department or alongside your in-house team. As consultants, we scope and deliver projects such as Microsoft 365 or Google Workspace migrations, network and server design, compliance readiness and IT strategy. You can start with either one.
You get one point of contact for everything technology-related, a helpdesk with unlimited tickets and plain-English updates whenever something changes. Behind the scenes, we monitor your systems around the clock, keep them patched and documented, and deal with your vendors for you. Every quarter, we sit down with you to review risk, roadmap and budget against your business goals.
Managed IT is a proactive, flat-fee service: your provider monitors, patches, secures and supports your systems continuously, before problems reach users. Break-fix IT bills hourly only after something breaks, which makes costs unpredictable and leaves security gaps between incidents. Alpiba is a managed IT provider.
Either way works. Alpiba can be your full outsourced IT department, or a co-managed partner that augments your internal IT staff with cybersecurity, cloud expertise and after-hours coverage while your team keeps ownership of day-to-day priorities.
Yes. Alpiba's Managed IT and White-Glove Support includes a tailored helpdesk plus on-site support for San Diego clients, with clear service-level agreements. You get a single point of contact for all of your technology needs.
Yes. Our Microsoft-certified and Google Workspace-certified engineers handle onboarding, email and file migration, security hardening, user training and ongoing administration for both platforms, including moves between them.
We deploy immutable, off-site backups that ransomware cannot encrypt or delete, test restores every quarter, and document a disaster recovery playbook for your business so you know exactly how and how fast systems come back after an outage, breach or hardware failure.
Both are strong platforms, and the right choice depends on how your team works. Microsoft 365 suits businesses that rely on desktop Office apps, complex spreadsheets or software that expects Exchange and SharePoint. Google Workspace suits teams that collaborate mostly in the browser and value simplicity. Our engineers are certified in both, so we can recommend one on its merits and migrate you in either direction.
Yes. AI assistants such as Copilot and Gemini can find anything a user already has access to, so files that are overshared today become easy to surface tomorrow. We start by reviewing and tightening permissions, then help you write a short AI usage policy and roll the tools out in stages, beginning with a pilot group. Sensitive automated actions keep a human approval step.
Remote and hybrid staff get the same support as the office: remote helpdesk sessions, 24/7 monitoring of their devices and accounts, and identity-first security that checks the user and device at every sign-in, wherever it happens. That matters across San Diego County, from North County to the South Bay, where many teams split their week between home and the office. When something needs hands-on work, on-site support is available for San Diego clients.
Yes. Our managed IT service includes vendor management and procurement. We deal with your internet provider, software vendors and equipment suppliers on your behalf, track renewals and licenses, and source hardware and software that fit your standards. When a problem sits between two vendors, you make one call and we own the follow-up, instead of you relaying messages between companies.
In most cases, yes. Microsoft and Google keep their services running, but deleted, overwritten or maliciously encrypted data can only be recovered within each platform's retention settings, which are limited and managed by the same admin accounts an attacker would target. An independent, immutable backup gives you copies you control, on your own schedule. We include cloud data in the backup plans we design.
Alpiba's SOC monitors 24/7 with an average first response under 15 minutes. For active ransomware or breach events, we trigger a documented containment playbook within the first hour.
A Security Operations Center (SOC) is a team that watches your systems around the clock, investigates alerts and contains threats. Alpiba runs a human-staffed SOC: real analysts monitoring your endpoints, identities, email and cloud 24/7, hunting anomalies and communicating clearly when something moves.
We layer defenses: managed EDR/XDR on every endpoint, identity, email and phishing protection, MFA and zero-trust access everywhere, continuous patching, immutable backups with quarterly-tested restores, and a documented ransomware containment playbook that our SOC executes within the first hour of an event.
EDR (Endpoint Detection and Response) watches each laptop and server for malicious behavior and can isolate a device instantly. XDR (Extended Detection and Response) correlates signals across endpoints, email, identity and cloud. Together they catch attacks that traditional antivirus misses. Alpiba deploys managed EDR/XDR across every endpoint.
Zero trust means no user or device is trusted by default, even inside your network. Every access request is verified by identity, device health and least-privilege rules, with multi-factor authentication everywhere. Alpiba builds zero-trust access into every environment we manage.
Disconnect affected computers from the network by unplugging the cable or turning off Wi-Fi, but don't wipe, rebuild or shut them down unless your security team says to. Then call your IT or security provider immediately, and notify your cyber insurer's incident line if you have one. Don't contact or pay the attackers. For managed clients, our SOC triggers a documented containment playbook within the first hour.
Make it a rule that new or changed payment details are confirmed by phone, using a number you already have on file, never one from the email. Then back the rule with technology: MFA on every mailbox, filtering that flags look-alike domains, SPF, DKIM and DMARC on your own domain, and training so finance staff recognize pressure tactics. Some of these emails come from real vendor accounts that have been hijacked.
Yes. A password manager is one of the simplest ways to stop password reuse, which is how a breach at one website turns into a break-in at your email or bank. It creates a unique password for every account, shares team logins safely instead of spreadsheets or sticky notes, and lets you revoke a departing employee's access centrally. Pair it with MFA for the strongest protection.
Protect the company data rather than the whole phone. Conditional access can require a passcode, a current operating system and an approved email app before a personal device connects, and app protection policies keep work data inside work apps. If the phone is lost or the employee leaves, you remove company data without touching their photos. Unmanaged devices can also be limited to browser-only access.
MFA fatigue is an attack in which someone who already has a password floods the user with sign-in approval prompts, hoping they tap Approve just to make it stop. Prevent it with number matching or phishing-resistant methods such as passkeys and security keys, sign-in rules that block risky locations, and training that tells staff to report unexpected prompts at once. Our SOC also watches for repeated prompt patterns.
Yes. We help clients design, implement and evidence the technical controls required by SOC 2, ISO 27001, HIPAA, NIST CSF and PCI DSS, and we keep audit trails ready for your auditor. Dental and healthcare-adjacent clients get HIPAA-aligned safeguards by default.
The frameworks we list describe the standards we build toward for our clients. They indicate readiness and controls alignment for client environments, not a third-party attestation of Alpiba as a company. Ask us for details on how we secure our own operations.
Yes, if the practice is a covered entity, which includes most providers that bill insurance electronically, and practice size doesn't change that. The HIPAA Security Rule calls for administrative, physical and technical safeguards to protect electronic patient information, beginning with a documented risk analysis. Compliance remains the practice's responsibility. We help by putting HIPAA-aligned safeguards in place, such as MFA, encryption, tested backups and access controls, and keeping the evidence organized.
In most cases, yes. Under HIPAA, an IT provider that creates, receives, maintains or transmits electronic patient information on your behalf is a business associate, and you need a signed business associate agreement before giving it access. The same applies to cloud, backup and email services that store patient data. Keep every agreement on file and review them whenever services or vendors change.
It applies if you are a for-profit business doing business in California and meet at least one threshold: annual revenue above the level set in the law, buying, selling or sharing the personal information of a large number of California consumers or households, or earning a significant share of revenue from selling or sharing it. The law, as amended by the CPRA, also expects reasonable security. Confirm whether it applies to you with legal counsel.
A SOC 2 Type I report describes your controls and whether they are suitably designed at a single point in time. A Type II report goes further, testing whether those controls actually operated effectively over a period of months. Enterprise customers often ask for Type II. Both are issued by an independent CPA firm; we help you prepare the controls and evidence, not issue the report.
Yes, on the security side. We help you put the controls insurers commonly ask about in place, such as MFA, EDR, immutable backups with tested restores, patching, staff training, a written incident response plan and round-the-clock alert monitoring, and we document the evidence so your answers are accurate. We don't sell insurance or advise on policy terms; your broker handles that. Our free cyber insurance readiness check is a good place to start.
Not unless the tool has been approved for that data under a written agreement and policy. Free public AI tools may keep prompts or use them to improve their models, and they typically aren't covered by agreements such as a HIPAA business associate agreement. Publish a short AI usage policy listing approved tools and what data each may handle, and give staff a sanctioned alternative so they aren't tempted to improvise.
Flat, per-user monthly pricing with no surprise line items. After a free assessment we scope a right-sized plan, so your IT budget stays predictable as your team grows.
In about 30 minutes we map your current risks, identify quick wins and outline a right-sized IT and security roadmap for your business. There is no obligation and no sales pressure.
Managed clients get 24/7 security monitoring and support. Our office line is staffed Monday to Friday, 7am to 7pm Pacific Time. Call 858-399-4225 or email info@alpiba.com.
We reply to every inquiry within 12 to 24 hours. For urgent issues such as an active incident, call 858-399-4225 to reach a senior engineer, not a call queue.
Onboarding follows our four-step process. In Discovery and Analysis we map your users, devices, software and vendors and note quick wins. In Solution Design we agree how support will work and which improvements come first. During Implementation we deploy monitoring and security tools, document your environment and set up onboarding and offboarding workflows, working in tight windows. Then Protect and Optimize begins: ongoing support, patching and quarterly reviews.
Plan the handover around access. Make sure your domain, DNS, cloud admin, firewall and backup accounts are registered to your business, then request credentials and documentation from the outgoing provider. We deploy monitoring and verify backups before anything old is removed, run a test restore, then rotate passwords and remove the previous provider's access. The aim is that your team keeps working throughout while we coordinate the details.
The flat per-user monthly price covers ongoing work: 24/7 monitoring and alerting, unlimited helpdesk tickets, patching, documentation, vendor management, onboarding and offboarding, and quarterly business reviews, plus the security services in your plan. Larger one-time work, such as a migration, a network refresh or a new office, is usually scoped and quoted up front, so you know the cost before it starts. Nothing arrives as a surprise line item.
You leave with a clear picture of your biggest risks, the quick wins worth doing now and a right-sized roadmap, whether or not you work with us. If managed IT or a specific project makes sense, we scope it and give you flat, per-user pricing. There is no obligation, and if managed IT isn't the right fit yet, we'll say so.
Budget IT per person, then add planned projects. With per-user pricing, your monthly cost grows in step with headcount, so hiring plans double as IT plans. On top of that, plan a refresh cycle for laptops and network equipment, license changes and known projects such as a new office or a migration. We review the roadmap and budget with you every quarter, so surprises show up as plans, not invoices.
No questions match that search. Ask us directly.
This managed IT FAQ is meant to be read before a first call, not instead of one. It covers who we are, what each service includes, how we approach security and compliance, and what pricing and onboarding involve, so you can spend that call on your own situation.
Answers are grouped into five topics, and each one starts with the direct answer before adding the context you need to act on it. Topics in the managed IT FAQ range from Microsoft 365 versus Google Workspace and AI tools at work to HIPAA for small practices, cyber insurance renewals, switching IT providers and the first steps to take if you suspect ransomware.
Where a topic needs more room, our guides, free tools and service pages go deeper. If the managed IT FAQ doesn't cover your situation, call our San Diego team at 858-399-4225, Monday to Friday from 7am to 7pm Pacific, or email info@alpiba.com. We reply to every inquiry within 12 to 24 hours.
Explore services
Managed IT
Your single point of contact for all technology, with a tailored helpdesk and on-site support backed by clear SLAs.
Learn more
Cybersecurity
24/7 monitoring, threat hunting and rapid incident response that contains attacks before they impact your business.
Learn more
Cybersecurity
Real analysts and real playbooks watching your endpoints, identities, email and cloud around the clock.
Learn more
Cloud & Productivity
Certified onboarding, migration, security hardening and ongoing administration by Microsoft-certified professionals.
Learn more
Infrastructure & Continuity
Immutable backups, tested restore plans and disaster recovery playbooks so your business stays online.
Learn more
Compliance & Risk
Design, implement and evidence the controls auditors and insurers ask for, and keep the audit trail ready.
Learn moreIndustries we serve
Protect research IP, lab instruments and audit-ready data.
IP protection · Lab uptime
Confidential files and secure access from anywhere.
Confidentiality · Remote access
Floor-system uptime and multi-site networks.
Uptime · Multi-site
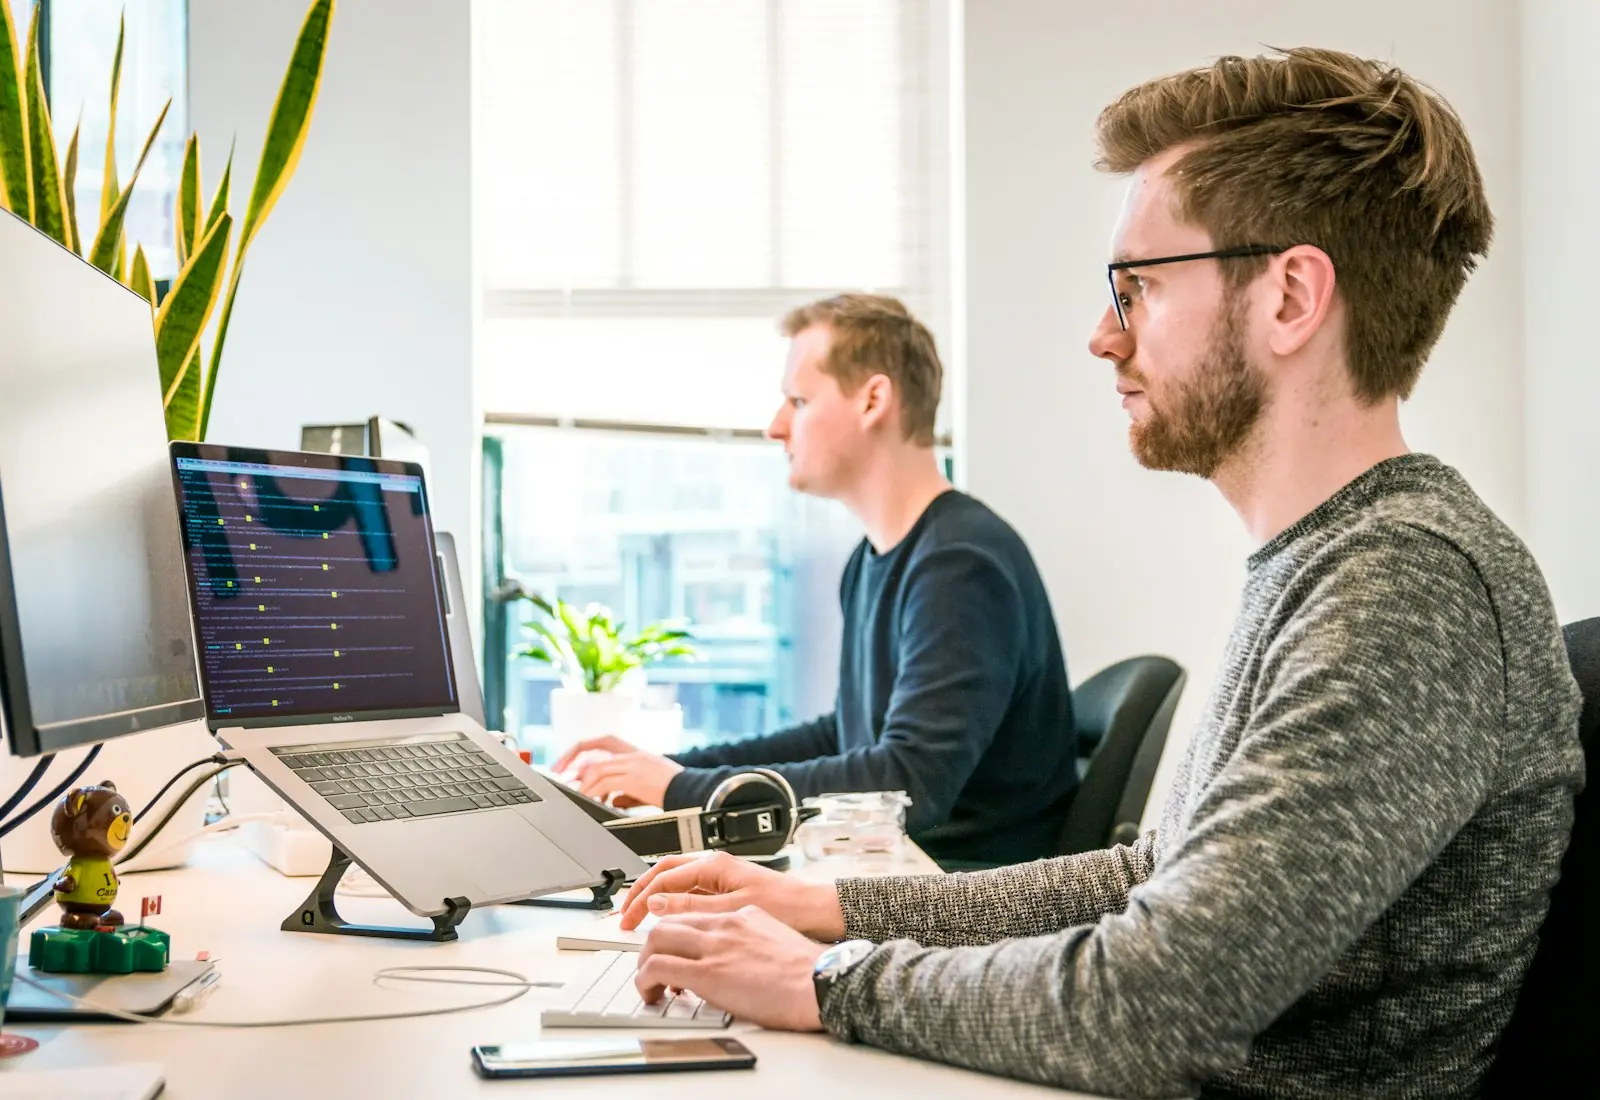
SOC 2 readiness and secure developer access.
SOC 2 · Cloud security

HIPAA-aligned safeguards for patient records.
HIPAA · Patient data
“SMBs deserve a strategic technology partner, without enterprise complexity or cost.”
Roopa · Founder, Alpiba · former Accenture advisor
If your question is not here, ask us directly. Callers reach a senior engineer, not a call queue.
Free 30-minute assessment
Tell us a little about your business. A senior engineer will map your top risks, quick wins and a right-sized plan, with no obligation and no sales pressure.

Founder-led and San Diego basedRoopa founded Alpiba to give growing businesses a real technology partner.