The cycle in plain English
- Inventory
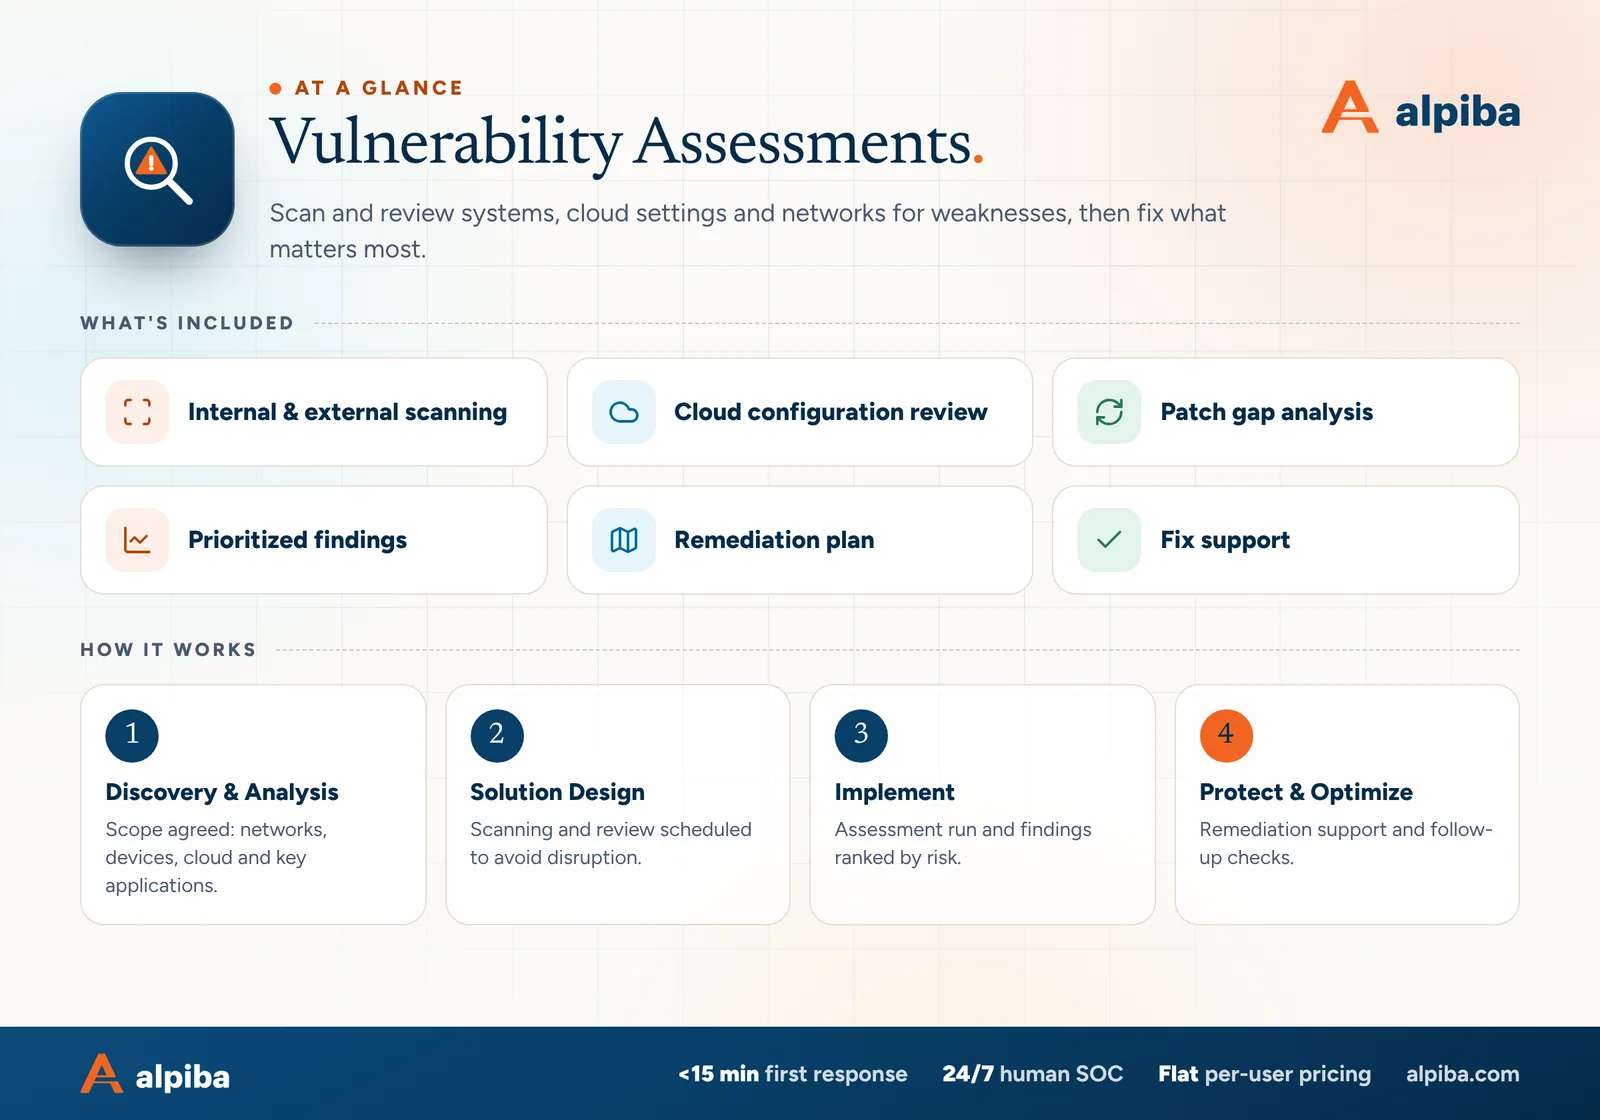
Know what you have: devices, servers, cloud services, internet-facing systems and the software they run.
- Scan
Check those assets for known weaknesses, from outside the network and inside it.
- Prioritize
Rank findings by exposure, real-world exploitation and business impact, not by severity score alone.
- Fix
Patch, reconfigure, isolate or retire, with an owner and a target date for every item.
- Verify
Re-scan to confirm each fix actually worked.
- Report
Keep a record of what was found, fixed and accepted, and review it with leadership.
The cycle never finishes. New vulnerabilities are published every day, and your environment changes every month. The goal is a steady rhythm you can sustain, not a perfect score.
Decide who does what before you start. A simple split works: one person, often the office manager or IT lead, owns the process and the log; your IT provider or internal team runs the scans and the fixes; leadership approves exceptions and reads the quarterly summary.