<1 hr
Attacks contained fast
Ransomware and breach events trigger a documented containment playbook within the first hour.
SOC online 24/7Breach or outage? Call 858-399-4225
Free guidesinfo@alpiba.comMon–Fri, 7am–7pm PT
Cybersecurity
Layered protection across your whole environment, with 24/7 monitoring, threat hunting and rapid incident response. When something happens, we contain it fast, communicate clearly and get you back to normal.
<15 min average first response Flat per-user pricing Free guide: The San Diego Ransomware Defense Playbook
The complete guide
Ransomware rarely arrives as one dramatic event. It's usually a chain: a stolen password or a convincing email, a quiet foothold on one laptop, a stretch of looking around that can last hours or weeks, and only then the encryption and the ransom note. Our cybersecurity services in San Diego are designed around that chain. Each layer, from identity and email to endpoints, backups and 24/7 monitoring, is there to break a specific link, so a single miss doesn't become a business-stopping event.
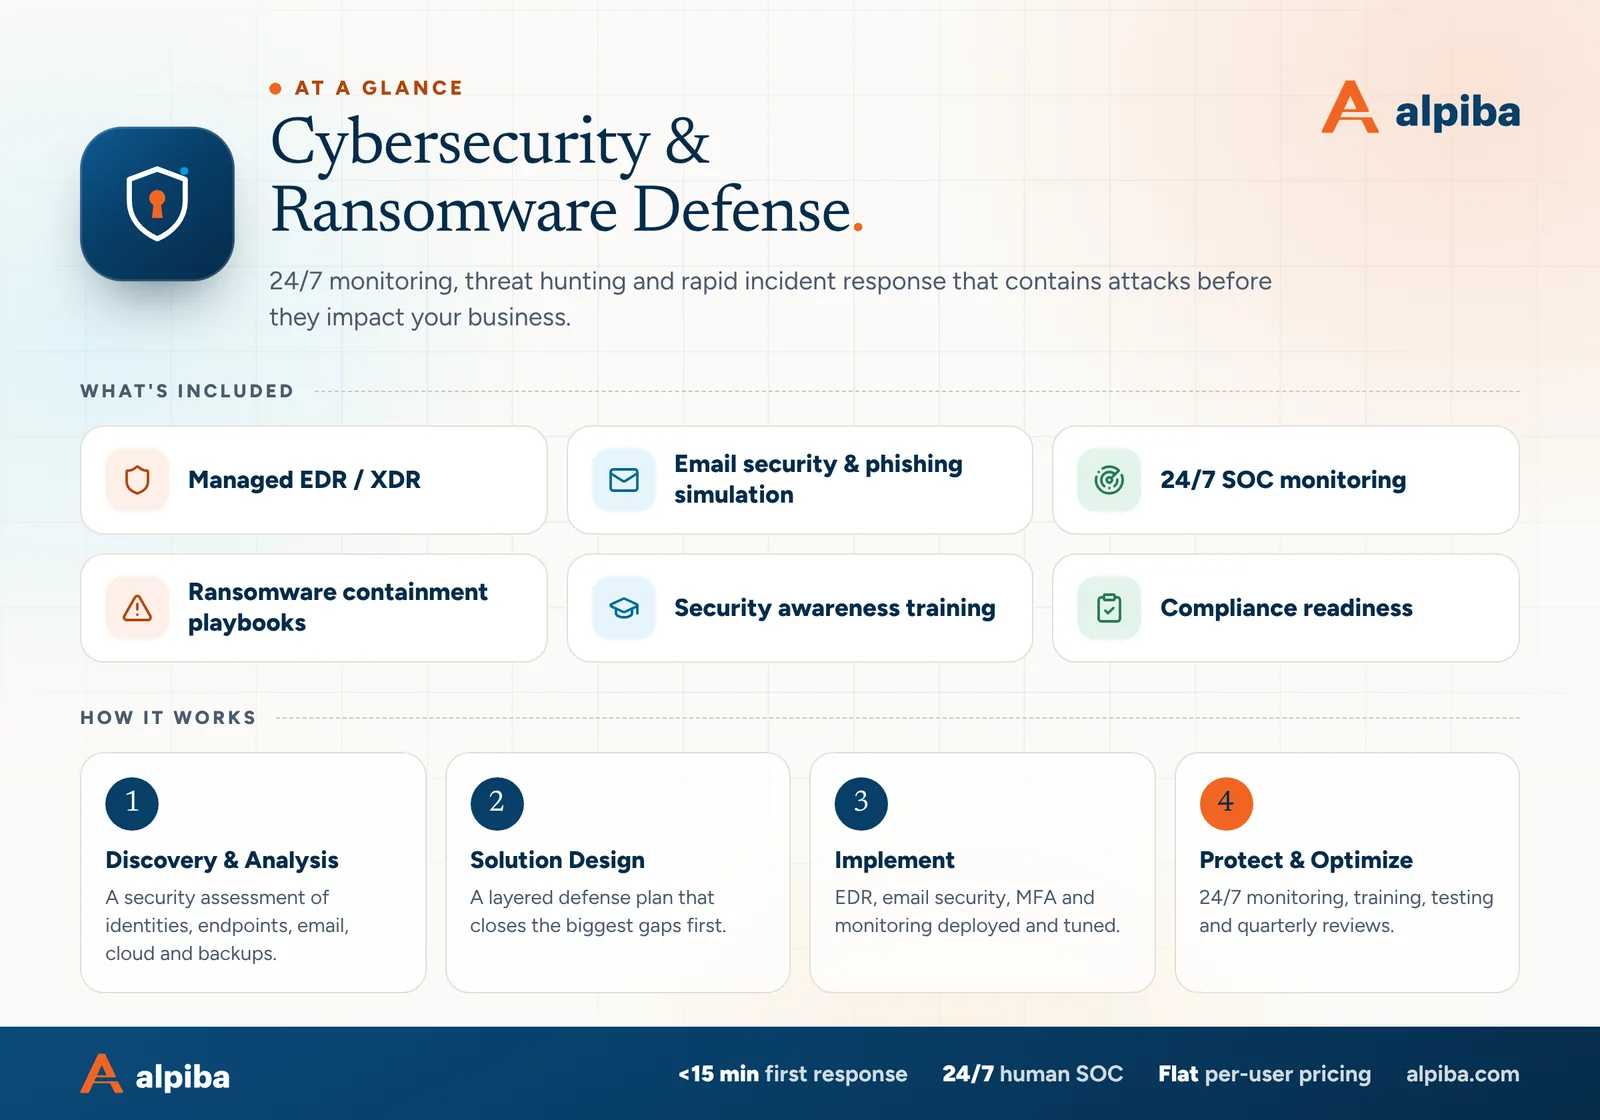
We built the service for growing businesses that hold sensitive data without a security department of their own: dental and law practices, biotech labs, manufacturers and software companies. It includes managed EDR/XDR, email security and phishing simulation, security awareness training, a human-staffed SOC with an average first response under 15 minutes, and a documented containment playbook we trigger within the first hour of a ransomware or breach event.
Below, we explain each layer in plain English, walk through how an attack typically unfolds and lay out the first-hour steps to take if it ever happens to you.
No single product stops every attack. Filters miss some phishing, people click, and new vulnerabilities appear before patches do. Layered defense accepts that and arranges controls so each one catches what the one before it missed. Here is what each layer does, in plain terms:
Identity and email do much of the work of keeping attackers out; backups decide how bad a bad day gets. That's why MFA and conditional access and phishing simulation and awareness training come early in any plan we build.
Traditional antivirus compares files against known threats. Many modern attacks use stolen accounts and legitimate admin tools that look normal to a file scanner, which is why behavior-based EDR and human review matter.
Ransomware groups operate like businesses, and most attacks follow a recognizable sequence. Knowing it shows where each layer earns its place. The earlier the chain breaks, the smaller the incident.
| Stage | What the attacker does | What stops it |
|---|---|---|
| Getting in | Uses a phished or reused password, an unpatched firewall or VPN, or a malicious attachment | MFA and conditional access, email filtering, prompt patching of internet-facing systems |
| Foothold | Installs a remote-access tool on one machine, often disguised as normal IT software | EDR flags the behavior and isolates the device while the SOC investigates |
| Privilege escalation | Hunts for admin passwords cached on the machine or reused across systems | Separate admin accounts, least privilege, no local admin rights for daily users |
| Moving around | Maps file shares, servers and backups from the compromised account | Network segmentation and SOC review of unusual sign-ins and connections |
| Attacking backups | Deletes or encrypts backups and snapshots so you can't recover | Immutable, off-site backups that the attacker's credentials can't reach |
| Stealing data | Copies sensitive files out to threaten publication later | Alerts on unusual data transfers, data loss prevention policies and least-privilege file access |
| Encryption and ransom | Encrypts systems, often overnight or on a weekend, and leaves a ransom note | Containment playbook, device isolation and restores from clean backups |
Notice that encryption is the last step, not the first. Everything before it is a chance to catch the attacker, which is why the early layers matter so much and why immutable backups with quarterly restore drills are the safety net when everything else has failed.
Encryption is often launched late at night, on weekends or over holidays, when nobody is watching and help is slow to arrive. That is the main reason round-the-clock monitoring is part of the service.
For a ransomware or breach event, the SOC starts a documented containment playbook within the first hour. Containment means stopping the spread and protecting what you need to recover, while keeping the evidence your insurer and investigators will ask for. The playbook sets these steps in motion:
An analyst validates the detection, declares an incident and starts a written timeline of every action taken.
Affected devices are cut off from the network through EDR while staying reachable for investigation. Compromised accounts are disabled and their sessions revoked.
Backups are checked to confirm the immutable copies are intact, and administrative access to them is locked down.
Logs, alerts and affected systems are preserved rather than wiped, because forensic investigators, insurers and law enforcement may need them.
Your named contact gets a plain-English call covering what we know, what we've done and what needs your decision. Restores are then sequenced by business priority.
Triggered within the first hour means the playbook is running, not that the incident is over. Investigation, cleanup and restores continue for as long as the evidence requires, and you get regular plain-English updates until systems are back and the way in has been closed.
Actions with business impact, such as taking a line-of-business server offline, are agreed with you in advance or confirmed on that call. Our 24/7 SOC and MDR service page explains how alerts are triaged and how those approvals are set.
If someone sees a ransom note, files renamed with strange extensions or a screen they don't recognize, the next few minutes matter. Print this list and keep it somewhere that doesn't depend on your network.
Whether you must notify customers, patients or regulators depends on what data was involved. California has its own breach notification law, and patient data falls under HIPAA's separate breach rules. Those decisions belong to you and your counsel; we supply the technical facts they need. A written incident response plan makes every one of these steps faster.
Insurers look at your security twice: when you apply or renew, and again when you make a claim. Our cyber insurance readiness check covers the application side, control by control. Once an incident starts, a different set of expectations applies, and they're written into the policy itself.
| Moment | What insurers commonly expect | How we support it |
|---|---|---|
| Application and renewal | Accurate answers about MFA, EDR, backups, patching, training, planning and monitoring | Coverage reports for each control, kept current for managed clients |
| First hour | Prompt notice through the claims line, often before outside help is engaged | The playbook timeline records when the incident began and every action taken |
| Investigation | Use of the insurer's approved forensic firms and breach counsel | We work alongside the panel firms and hand over logs and preserved evidence |
| Payment decisions | No ransom negotiation or payment without the insurer's consent | Containment and restores from immutable backups, so paying isn't your only option |
| Recovery and claim | Records of costs, downtime and the steps taken | A written incident timeline and a plain-English summary of the response |
Notice deadlines, approved-vendor rules and consent requirements live in the policy wording. Note them on your contact sheet before anything happens, and make sure your IT provider knows them too.
Insurer expectations and good security mostly point the same way, so closing the gaps an underwriter asks about is rarely wasted effort, even in a year when your premium doesn't move.
Many businesses already own some of these tools. The gaps tend to be in coverage, configuration and who watches the alerts. Every engagement starts with a security assessment of identities, endpoints, email, cloud and backups, then closes the biggest gaps first, with changes made in tight windows so work keeps moving.
Starting from a typical small-business setup, this order closes the most common gaps fastest:
After that, the work is steady rather than dramatic: round-the-clock monitoring, regular training and simulations and quarterly restore drills, with progress tracked against the measures below.
Security reports love big numbers: threats blocked, emails scanned, attacks stopped. Those figures say more about the internet than about your business. Better measures track coverage and speed for the things you control, and they should improve quarter over quarter.
The share of accounts with MFA enforced, including admin and service accounts. The goal is every account, with any exception written down and reviewed.
Devices reporting to EDR compared with your asset inventory. A laptop that hasn't checked in recently is a blind spot worth chasing.
How long critical updates take to reach every device after release. Track the slowest machines, not just the average.
The date and outcome of the last restore drill for each key system. Compare how long recovery took with the target you agreed.
How quickly access is removed when someone leaves. Same day is the standard worth holding.
How many people report a simulated phish, not just how many click. A rising report rate means your team has become an early warning system.
We review these with you in plain English at quarterly reviews, along with any incidents and what changed because of them. If a measure moves the wrong way, you'll hear why and what we're doing about it.
The fundamentals are the same everywhere, but a few local realities change the details of cybersecurity services in San Diego.
Being San Diego-based also means we can be on-site when an incident needs hands on equipment, from replacing a compromised workstation to reconnecting a cleaned network, while 24/7 monitoring covers your team wherever they work.
The gaps that matter are rarely exotic. Usually they're controls that exist but don't cover everything:
When you compare cybersecurity services in San Diego, ask questions that force specific answers:
Our pricing is flat per user each month, and the scope reflects your users and devices, how sensitive your data is and the compliance obligations you carry. Our security health check gives you a quick score today, and a vulnerability assessment shows exactly what an attacker would find.
Talk to an engineer
Free 30-minute assessment. We reply within 12–24 hours.
“SMBs deserve a strategic technology partner, without enterprise complexity or cost.”
Roopa · Founder, Alpiba · former Accenture advisor
Alpiba is founder-led. Every Cybersecurity engagement starts by listening to how your business runs, and senior engineers stay with you from the first call onward.
Free guide · PDF
A printable playbook for business owners and the people who run their offices and IT: what to put in place before an attack, what to do in the first hour and how to recover.
Get the free guide
Related services
Cybersecurity
Real analysts and real playbooks watching your endpoints, identities, email and cloud around the clock.
Cybersecurity
Filter malicious email, run phishing simulations and train your team to spot what gets through.
Infrastructure & Continuity
Immutable backups, tested restore plans and disaster recovery playbooks so your business stays online.
Built for regulated teams
Free 30-minute assessment
Tell us about your business and what prompted the search. A senior engineer will reply within 12–24 hours to set up your free 30-minute assessment.
Founder-led and San Diego basedRoopa founded Alpiba to give growing businesses a real technology partner.