SOC online 24/7Breach or outage? Call 858-399-4225

Free guidesinfo@alpiba.comMon–Fri, 7am–7pm PT

Alpiba

Free service guide · PDF

The SOC 2, HIPAA and NIST CSF Readiness Roadmap

A practical path from the first questionnaire to audit-ready evidence, whichever framework your customers or regulators expect.

  • How to tell which framework you need from the requests you're receiving
  • A six-stage roadmap from scoping to audit and beyond
  • A control map showing where one control serves SOC 2, HIPAA and NIST CSF
  • A readiness checklist, partner questions and a 90-day plan

12 pages27-item checklist30/60/90-day plan

Cover of The SOC 2, HIPAA and NIST CSF Readiness Roadmap

Get your free copy

Instant PDF download. No sales pitch inside.

Instant download. By submitting, you agree that Alpiba may contact you about this guide; you can ask us to delete your details at any time.

Cover and two sample pages of The SOC 2, HIPAA and NIST CSF Readiness Roadmap, a free 12-page PDF guide from Alpiba with a 27-point checklist
A look inside: the cover and two pages from the 12-page PDF.

What's inside

Inside the guide.

SOC 2, HIPAA and NIST CSF look like three different projects. In practice they ask for many of the same things: named accounts with MFA, reviewed access, encrypted devices, monitored systems, tested backups, a rehearsed incident plan, vetted vendors and trained staff. The differences lie in who asks, who checks and what the finished result looks like.

This roadmap is written for founders, practice owners, operations leads and IT managers facing their first framework or tidying up after a rushed one. Use the first section to choose a starting point, treat the roadmap and control map as your working plan, and score yourself with the checklist. One reminder applies throughout: auditors and assessors reach their own conclusions, and your organization remains responsible for its compliance.

  1. Start with who is asking
  2. The six-stage readiness roadmap
  3. One control, three frameworks
  4. What good evidence looks like
  5. Keeping it running after the audit
  6. The checklist27 items in 5 groups
  7. Questions to ask any IT provider10 questions
  8. Your 30/60/90-day plan3 phases, step by step
  9. Plain-English glossary8 terms

Read Part 1 free

The opening chapter of the guide, in full. The rest of the guide, the checklist and the 90-day plan are in the PDF.

Start with who is asking

The fastest way to pick a framework is to look closely at the request in front of you. The wording usually tells you what will satisfy the person asking.

What the request usually means
If you hearYou probably needFirst move
“Please send us your SOC 2 report.”SOC 2, usually Type IIA readiness assessment, then a decision on Type I or Type II and the review period
“We need you to sign a business associate agreement.”HIPAA safeguards, as a business associateA HIPAA risk analysis and a review of how you handle patient data
“Please complete our security questionnaire.”Often no specific frameworkA NIST CSF baseline, so your answers are consistent and true
“Your renewal requires MFA, EDR and offline backups.”Your insurer's list of controlsClose those controls first and keep the evidence
“Which SAQ do you file?”PCI DSSConfirm your questionnaire type with your acquiring bank and map where card data flows

If you hear several of these, start with the one tied to the most revenue or the nearest deadline, then reuse its controls for the rest.

Get the full guide

A preview

A sample from the guide.

Here's the first checklist group and a few of the questions. The full guide has all 27 checklist items, 10 questions and the 90-day plan.

Scope and governance

  • We know which framework we need and who is asking for it
  • Scope is written down: systems, locations, people and data
  • A data flow diagram shows where sensitive data enters, lives and leaves
  • A named person owns the compliance program
  • A risk assessment was completed or updated in the last year
  • Core policies are approved and match how we actually work

Questions to ask any IT provider

  1. 1Will you work alongside an audit firm we choose, while keeping your readiness work separate from the audit?
  2. 2Which framework would you recommend for us, and why that one first?
  3. 3How will you define our scope, and what would you leave out?
  4. 4Who implements the technical controls, and who writes the documentation?

+ 6 more questions in the full guide

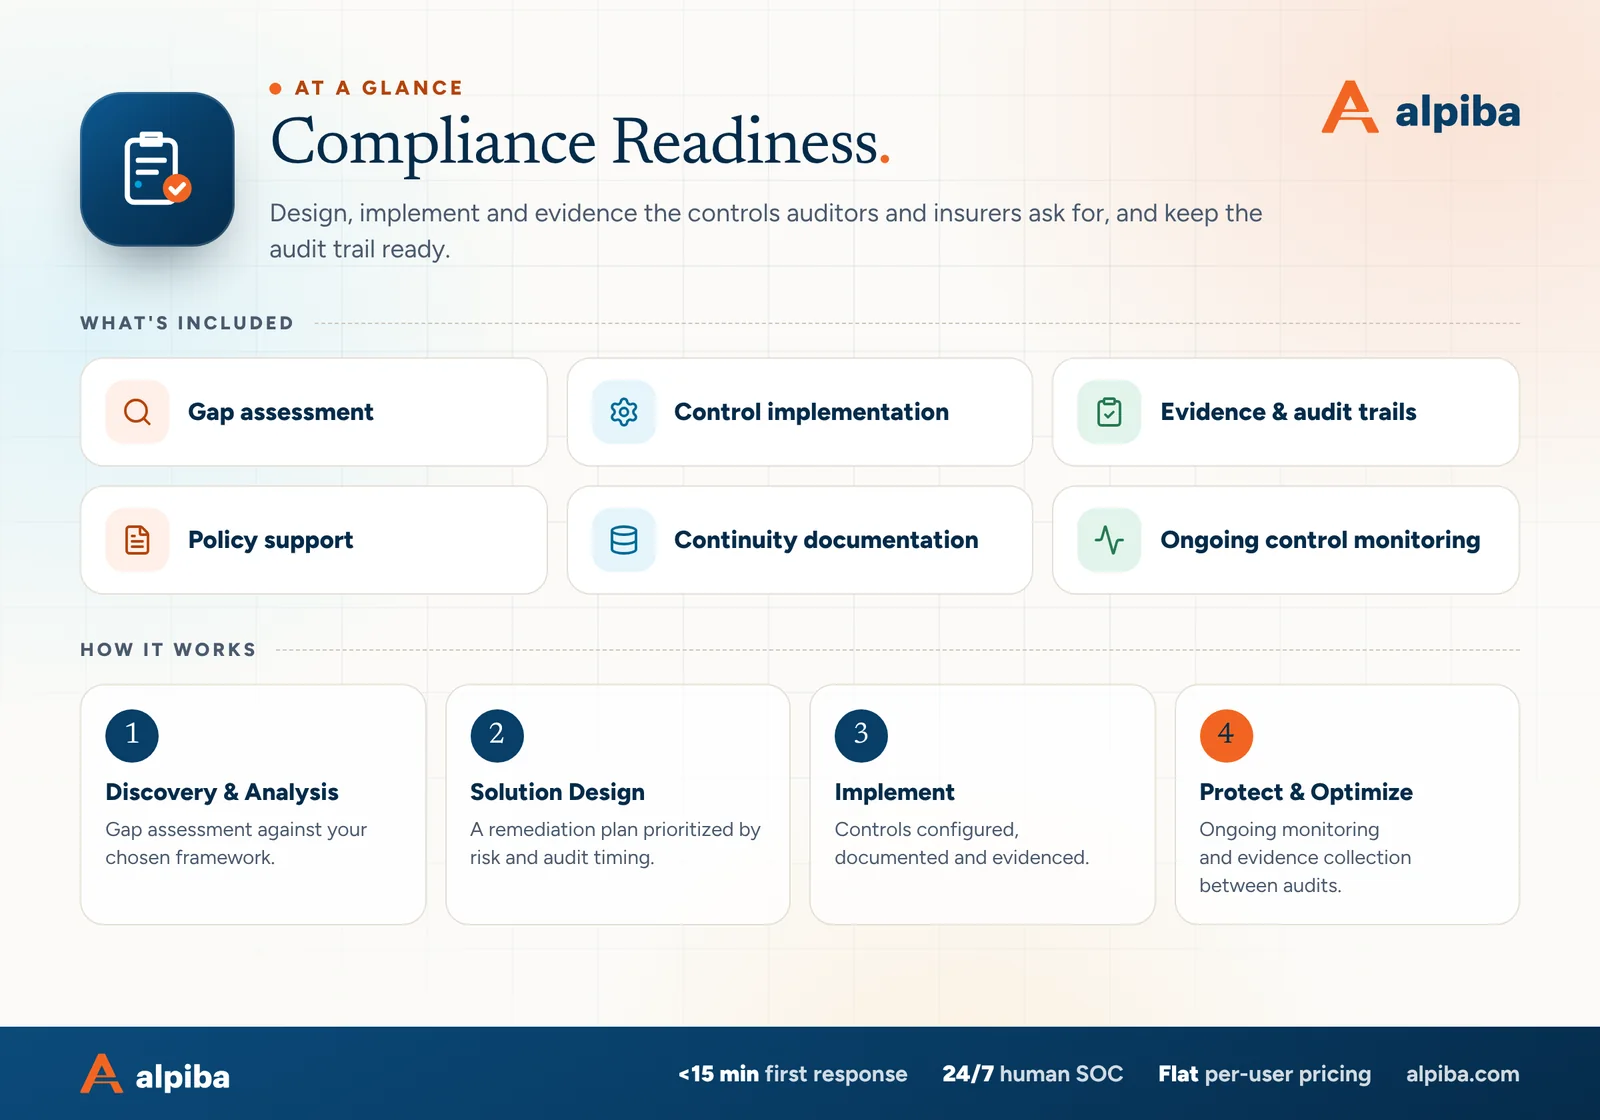
Compliance Readiness at a glance. Included: Gap assessment, Control implementation, Evidence & audit trails, Policy support, Continuity documentation and Ongoing control monitoring. How it works: Discovery & Analysis, Solution Design, Implement and Protect & Optimize.
Compliance Readiness at a glance: what is included and how we roll it out.

Your first 30 days

Where to start this month.

The guide's 30/60/90-day plan begins with these steps. Assign an owner to each and review progress every two weeks.

  • 1Identify who is asking and choose the framework
  • 2Write down the scope and draw the sensitive data flow
  • 3Run a gap assessment and rank the gaps
  • 4Turn on MFA everywhere it's missing

Key terms in plain English

Attestation report
A formal opinion from an independent auditor about your controls. A SOC 2 report is an attestation, not a certification.
SOC 2 Type II
A SOC 2 report that tests whether controls operated effectively over a review period, rather than at a single point in time.
Risk analysis
Under HIPAA, a documented assessment of the risks to electronic patient data and how they are addressed. It is the starting point for the Security Rule.
Business associate agreement (BAA)
A contract HIPAA requires when a vendor creates, receives, keeps or transmits protected health information for a covered entity.
Current and target profile
In NIST CSF, a description of how you perform today and where you want to be, used to plan improvements.
Control
A specific safeguard, such as MFA or a quarterly access review, that reduces a risk and can be tested.
Evidence
Records that prove a control exists and operated, such as dated exports, tickets, logs and sign-offs.
Scope
The systems, locations, people and data an audit or assessment covers. Getting scope right shapes the whole project.
Roopa, founder of Alpiba

SMBs deserve a strategic technology partner, without enterprise complexity or cost.RoopaFounder, Alpiba

Put the guide to work

Services that help you act on it.

All services
A team in a working session around a conference table

Compliance & Risk

Compliance Readiness

Design, implement and evidence the controls auditors and insurers ask for, and keep the audit trail ready.

Hands working on a laptop during a review

Compliance & Risk

Vulnerability Assessments

Scan and review systems, cloud settings and networks for weaknesses, then fix what matters most.

A close view of a computer circuit board

Infrastructure & Continuity

Backups & Business Continuity

Immutable backups, tested restore plans and disaster recovery playbooks so your business stays online.

Keep reading

More free guides.

All guides
Cover of The Vulnerability Management Starter Guide

Service guide · Vulnerability Assessments

The Vulnerability Management Starter Guide

A practical starter guide for owners and IT leads: build an asset inventory, set a scanning rhythm, rank findings by real risk and keep the records insurers and auditors ask for.

Cover of The San Diego Managed IT Buyer's Guide

Service guide · Managed IT

The San Diego Managed IT Buyer's Guide

A vendor-neutral workbook for San Diego owners and office managers choosing a managed IT provider: what to gather, what to ask, how to score proposals and how to run the first 90 days.

Cover of The Co-Managed IT Playbook

Service guide · Co-Managed IT

The Co-Managed IT Playbook

A practical playbook for IT leads and executives setting up a co-managed partnership: a responsibility matrix, access rules, an escalation runbook and the metrics that show whether it is working.

Call Free assessment