What buyers and auditors actually ask
Enterprise security reviews come in three common forms: a custom questionnaire from the customer's procurement or security team, a standardized questionnaire (the Standardized Information Gathering questionnaire, or SIG, and the Consensus Assessments Initiative Questionnaire, or CAIQ, are common examples), and a request for an independent report such as SOC 2 or an ISO 27001 certificate. The formats differ, but the questions behind them repeat.
- Identity: Is MFA enforced everywhere? Do you use single sign-on? Are admin accounts separate? How fast is access removed when someone leaves?
- Devices: Are laptops company-managed, encrypted, patched and protected by EDR? Can a lost laptop be locked or wiped?
- People: Do employees complete security training and acknowledge written policies? Are contractors held to the same rules?
- Data: Where does customer data live, who can reach it, and how is it protected in transit and at rest?
- Response: Who watches for threats around the clock? Is there an incident response plan? Are backups tested?
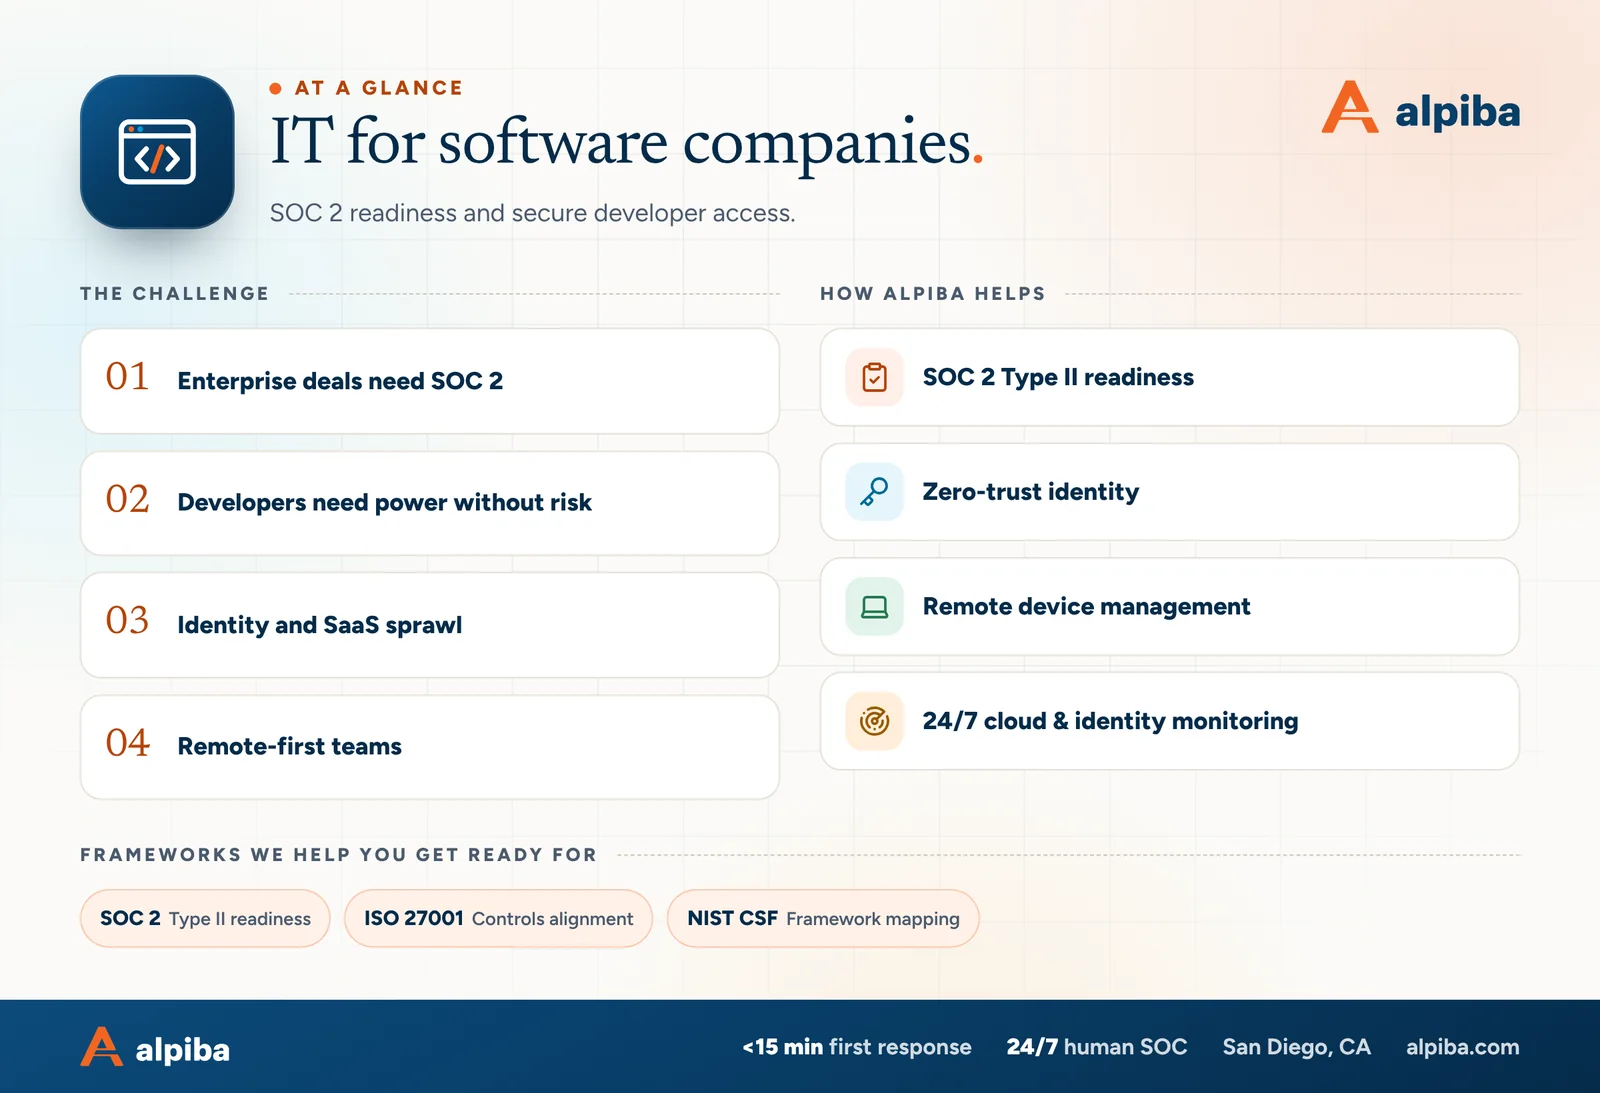
Behind many of these requests sits SOC 2, an attestation from an independent CPA firm measured against the AICPA's Trust Services Criteria. Security is the required category; availability, processing integrity, confidentiality and privacy are optional additions. A Type I report evaluates the design of your controls on a single date. A Type II report also tests whether they operated effectively over an observation period, commonly three to twelve months, so controls need to be running well before you want the report.
Put the product and systems customers rely on in scope, and add optional criteria only when customers ask for them. A tight scope is cheaper to evidence and easier to keep running every year.